Risk advisory for the parts of the organisation the perimeter doesn’t cover.

Scutaria is an independent practice based in Switzerland. It helps security leaders, general counsel and boards get a grip on third-party risk, insider risk and the overlap between cyber and physical security, in whichever jurisdictions they operate.

The name comes from the scutum, the Roman legionary’s shield: it protected the soldier, and in formation it protected the people next to him. Most risk today travels through suppliers, insiders and shared infrastructure. That is where the shield has to be.

Three risks that sit between functions, and fall between them.

Each of these is owned by several teams and fully by none. Scutaria works across security, legal, procurement, HR and operations to give them a single owner, a method and a measurable outcome.

Third-party risk

Suppliers, outsourcers, cloud platforms and agents now carry a large share of operational and data risk. Scutaria builds programmes that tier vendors by real exposure, assess them proportionately and keep the evidence regulators now ask for under DORA and NIS2.

Insider risk

Trusted people with legitimate access remain the hardest threat to detect and the most delicate to manage. Scutaria designs insider-risk programmes that are lawful, proportionate and defensible, with the right balance of HR, legal, security and monitoring.

Cyber-physical convergence

Access control, CCTV, building systems and OT are networked, and the teams running them rarely share a risk picture with the SOC. Scutaria brings twenty years across intelligence, physical security and cybersecurity to close that gap.
Three ways to work together, in increasing depth.

Most relationships start with a diagnostic. Some stop there with a clear plan; others continue into building the programme, and then into ongoing advisory once it runs. Fees are fixed per engagement and agreed up front.

When you need a clear, independent picture

Diagnostic

A focused assessment of your third-party, insider or converged-security posture against the regulations and standards that apply to you, ending in findings the board can act on.

  • Document and interview-based review of governance, process and tooling
  • Gap analysis against NIS2, DORA, FINMA, ISO 27001 or MAS TRM as relevant
  • Prioritised roadmap with effort and sequencing
  • Executive readout and written report

Typically four to eight weeks

When you need the programme built, not just described

Programme build

Design and stand up a third-party or insider-risk programme end to end: operating model, policies, assessment method, tooling selection and the handover to the team that will run it.

  • Governance, roles and decision rights across security, legal, procurement and HR
  • Tiering model, assessment questionnaires and contract clauses
  • Tool selection and configuration support
  • Pilot on a first wave of vendors or use cases, then scale

Typically three to nine months

When you want senior judgement on call

Advisory retainer

A fractional risk advisor for organisations that have a programme and want it to keep pace with the business, the threat and the regulator, without hiring a full-time senior role.

  • Agreed monthly days, used flexibly
  • Quarterly programme reviews and board or audit-committee preparation
  • Regulatory watch across Europe, Switzerland, the Gulf and Asia
  • Support during supplier incidents and insider investigations

Rolling, reviewed every six months

Regulatory reach beyond one jurisdiction.

Multinational organisations are asked the same questions by different regulators in different words. Scutaria maps those requirements once, so a single programme can answer all of them.

  • NIS2 Supply-chain security and reporting duties for essential and important entities
  • DORA ICT third-party risk and register of information for EU financial entities
  • FINMA circulars Outsourcing and operational-risk expectations for Swiss financial institutions
  • Swiss nFADP Data protection obligations for processors and controllers
  • ISO/IEC 27001 and 27036 Information security and supplier-relationship controls
  • MAS TRM Technology risk management for Singapore financial institutions
  • China MLPS and PIPL Multi-level protection scheme and personal-information rules
  • UAE and Saudi frameworks PDPL, NCA ECC and sector regulators in the Gulf
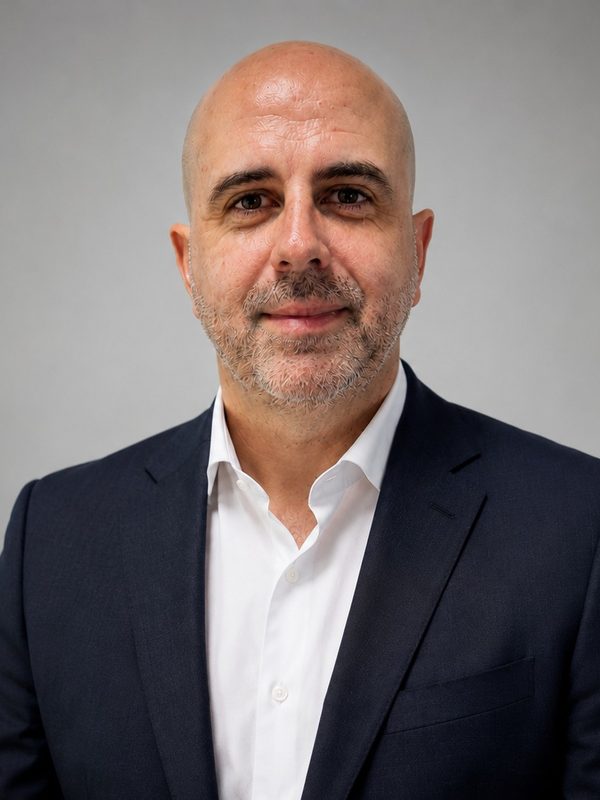
Eric Boyer, founder of Scutaria

Eric Boyer

Founder and senior advisor

Eric has spent twenty years in intelligence, cybersecurity and physical security, in government and in the private sector. He spent ten of those years in Asia, and has since worked on data-protection and security programmes for the Gulf, India and Europe with Richemont and Accenture.

That path is why Scutaria looks at risk the way it does: through the people who hold access, the partners who share it and the buildings and systems that connect them, rather than through any single control domain.

Eric works in French and English, from the Lake Geneva region, and travels where the work is.

  • CISSPCertified Information Systems Security Professional
  • CFECertified Fraud Examiner, member of ACFE Switzerland
  • ISO/IEC 27001 Lead ImplementerInformation security management systems
  • PreviouslyRichemont, Accenture, public-sector security and intelligence roles

Tell me what is keeping you up at night.

A first conversation is free and usually takes forty minutes. If Scutaria is not the right fit, you will leave with a straight answer and, where possible, a name of someone who is.